Malware
-
Breaches
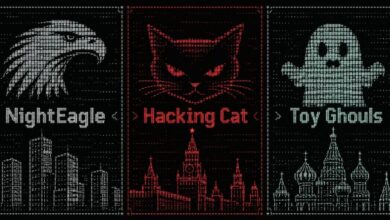
Three Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and Wipers
Enterprises in Russia have emerged as the target of three threat activity clusters tracked as NightEagle, Hacking Cat, and Toy…
-
Breaches
Cisco FMC Flaws Exploited to Steal Credentials and Deploy Qilin Ransomware
Ravie LakshmananSep 11, 2026Vulnerability / Malware Cisco has revealed that three distinct threat clusters linked to ransomware and state-sponsored attacks…
-
Breaches
WordlistLoader Delivers Amatera via ClickFix, SynkLoader Phishes Windows Passwords
Cybersecurity researchers have flagged two new malware families called WordlistLoader and SynkLoader that’s used to deliver next-stage payloads and likely…
-
Malware Analysis
Rare UEFI Malware Found in the wild Kaspersky says
By Mark Lechtik, Igor Kuznetsov, Yury Parshin Part II. Technical details (PDF) UEFI (or Unified Extensible Firmware Interface) has become a prominent technology…
-
Malware Analysis

IcedID Malware Updates new techniques To Avoid Detection
by Paul Kimayong In our previous blog about IcedID, we explored some of the changes in the malware and how it tries to…
-
Malware Analysis
New Info Stealer Poulight From The Russian Underground
Poulight Stealer, a new Comprehensive Data Stealer from Russia Introduction Nowadays, info-stealers are one of the most common threats. This…
-
Breaches
GodDamn Ransomware Uses PoisonX Driver to Disable Endpoint Defenses
Ravie LakshmananJul 09, 2026Malware / Endpoint Security Cybersecurity researchers have flagged a new ransomware family called GodDamn that employs the…
-
Breaches
AI Agent Exploits Langflow RCE to Automate Database Ransomware Attack
Security firm Sysdig says it has found what it believes is the first ransomware attack run from start to finish by an…
-
Breaches
Ransomware Groups Turn to Citrix Bleed 2, BYOVD, and Supply Chain Credentials
Threat actors associated with the Anubis ransomware operation have been observed exploiting the Citrix Bleed 2 (CVE-2025-5777) vulnerability to obtain…
 English
 العربية
 简体中文
 Nederlands
 Français
 Deutsch
 Italiano
 Қазақ тілі
 Кыргызча
 Latviešu valoda
 Lietuvių kalba
 Português
 Русский
 Српски језик
 Slovenčina
 Slovenščina
 Español
 Türkçe
 Українська
 O‘zbekcha